The Linux Forensic Journey — LiME (Linux Memory Extractor)

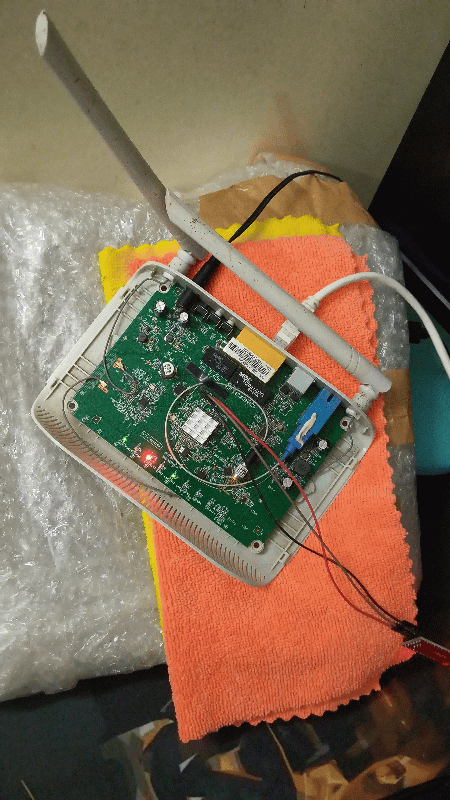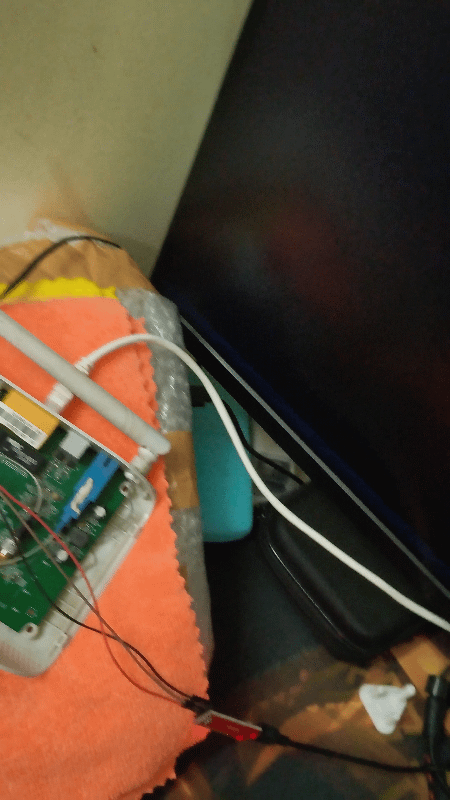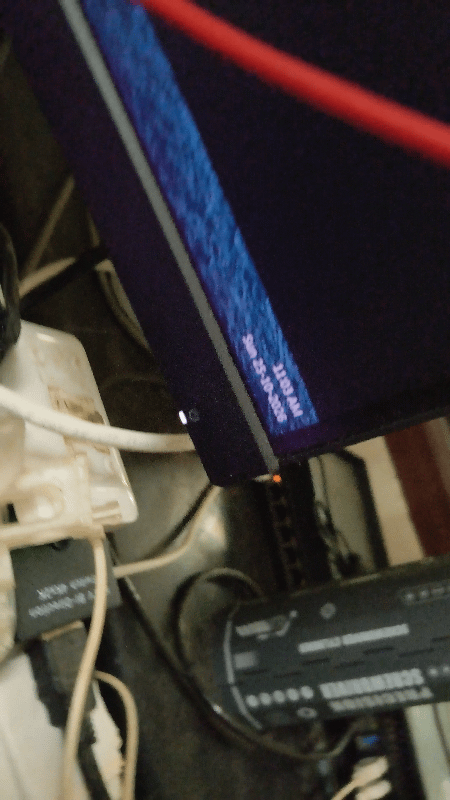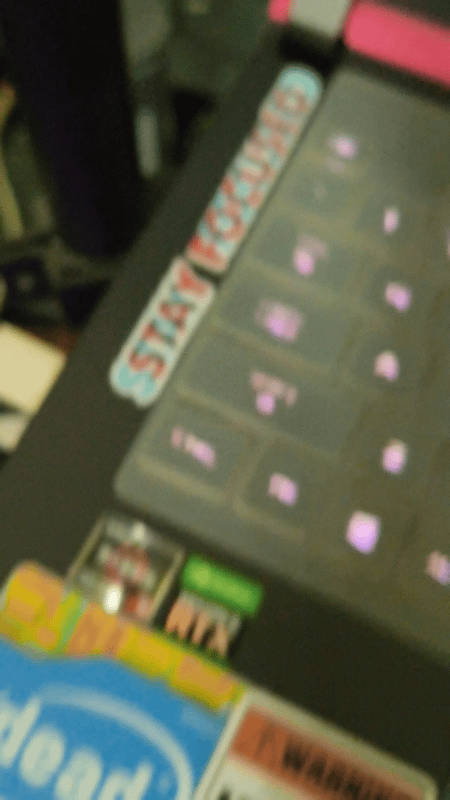
LiME (Linux Memory Extractor) is a specialized LKM (https://medium.com/@boutnaru/the-linux-concept-journey-loadable-kernel-module-lkm-5eaa4db346a1) designed for high integrity volatile memory acquisition across Linux\Android systems — as shown in the screenshot below (https://www.youtube.com/watch?v=Llsoo8LHhWg). It pioneered full memory capture for Android and remains a gold standard because it operates primarily in kernel space. By minimizing context switching between user and kernel modes, LiME reduces the “smearing” of data, ensuring the resulting image is more forensically sound and less altered by the acquisition process itself (https://www.levelblue.com/blogs/levelblue-blog/memory-dump-analysis-using-lime-for-acquisition-and-volatility-for-initial-setup).
Overall, LiME is a kernel mode acquisition tool designed for full volatile memory capture with a minimal process footprint to preserve forensic integrity. It supports local storage or remote acquisition using TCP. Thus, offering flexible output formats: “lime” (each range prepended with fixed-size header containing address space info) , “padded” (pads all non System RAM ranges with 0s) or “raw” (concatenates all System RAM ranges). LiMe also supports optional zlib compression to significantly reduce transfer times. It also provides the ability to further ensure data authenticity through integrated hashing (supporting algorithms like SHA-256 and MD5) and optimize performance using Direct IO and custom timeout settings (https://github.com/jtsylve/LiME).
Get Shlomi Boutnaru, Ph.D.’s stories in your inbox
Join Medium for free to get updates from this writer.
Lastly, The workflow begins with LiME to capture the physical memory, followed by an in-depth forensic analysis of the dump using Volatility (https://opensource.com/article/21/4/linux-memory-forensics). Beside LiMe there are also other memory dumping tools. AVML is the gold standard because it is a Rust based (static binary) that minimizes the forensic footprint without requiring kernel headers. If our investigation scales across a network, “LiMEaide” and “Margarita Shotgun” provide essential remote orchestration via Python, while Linux Expl0rer serves as a comprehensive live triage suite for hunting active threats with YARA (https://cybersectools.com/tools/lime) — more on those and others in future writeups.
See you in my next writeup ;-) You can follow me on twitter — @boutnaru (https://twitter.com/boutnaru). Also, you can read my other writeups on medium — https://medium.com/@boutnaru. You can find my free eBooks at https://TheLearningJourneyEbooks.com.