TryHackMe: Agent Sudo writeup

room link: https://tryhackme.com/room/agentsudoctf
Task 1: Enumeration
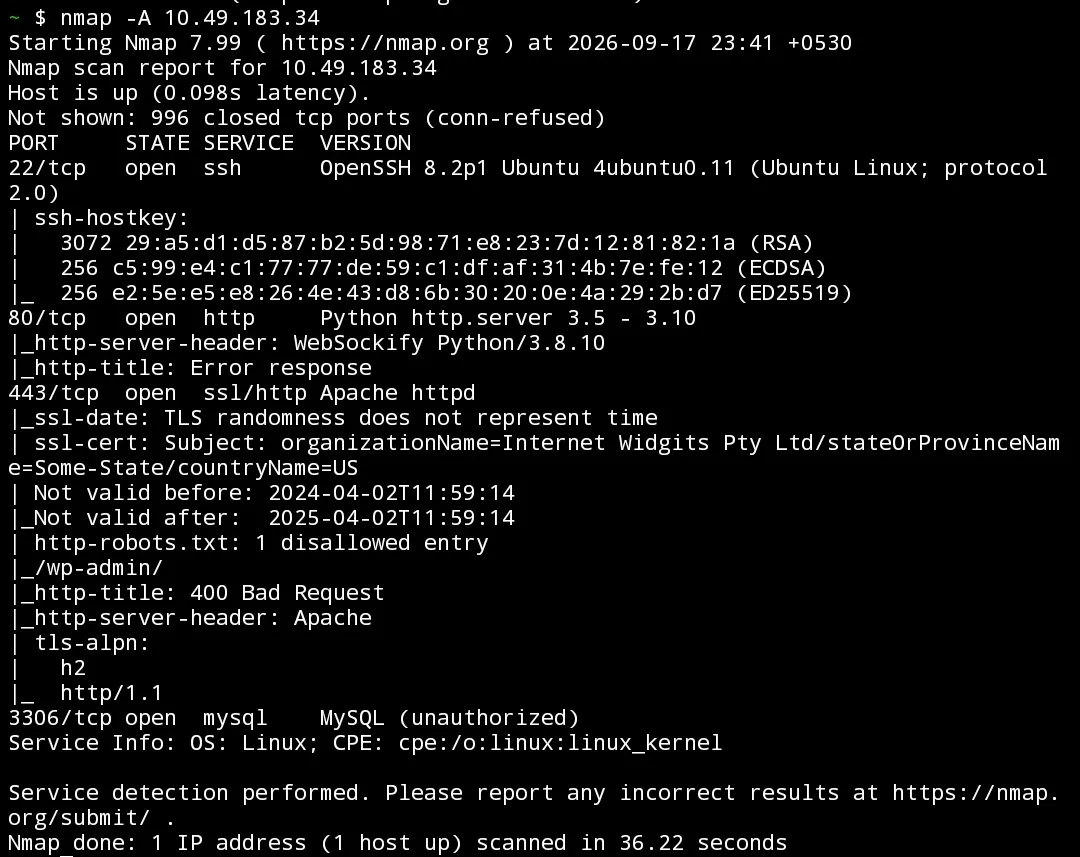
1. How many open ports?

3
2. How do you redirect yourself to a secret page?

user-agent
3. What is the agent name?
Chris
Got stuck, didn’t know what to look for. Got a hint:

In the networks tab, changing the value of User-Agent to C.


This leads to...

Task 2: Hash Cracking and Brute-force
1. FTP password
crystal

Let’s use these credentials.

Getting these files...

note: to escape- !

Clearly hinting to steganography.
Get cracka_xss’s stories in your inbox
Join Medium for free to get updates from this writer.
Extracting Hidden Files:

the other filed didn’t have anything. So.... We get a zip file. Let’s prepare and use John for the password.
Zip password:


There, our password is alien.
Now that we have the password, let’s go ahead and see what’s in the zip file.

Steg password
Decoding that with base 64 gives us Area51.
using that password...

Here, we get the other two flags.
3. Capturing the user flag
Using those SSH credentials...

4. Privilege Escalation
upon some investigations...


So, running ‘sudo -u#-1 /bin/bash’ should give us root access.