vantaroot·Oct 4Binary Exploitation: A Practical Guide to Memory, Buffers, and Control FlowBinary exploitation can sound complicated when you first encounter words such as stack frames, registers, return addresses, heap…
Natsuiro XCN·Nov 5, 2025SEC Playground Hackloween2025 CTF: Rev&Pwn-Pentest Writeupปีที่แล้วผมพลาดที่จะเข้าร่วมงานนี้ไป เพราะฉนั้น ในวันนี้เราจะมาดูโจทย์ในหัวข้อ Reverse Engineering กับ Pwnable-Pentest กันครับ~
Jez O'Donnell·Jan 29, 2025ReplaceMe Hack The Box WalkthroughUnzipping the zip gives us 5 files, a libc file and a binary file, a test flag and 2 docker related files
mirakiht·Nov 24, 2024Canary leak and Return to win — The Hacker Conclave v2 Pwn3 challengechecksec แล้วพบว่าเป็น elf 64 bit Canary found No PIE (0x400000)
mirakiht·Nov 24, 2024Overwrite GOT with format strings - The Hacker Conclave v2 Pwn2 challengechecksec ดูแล้วพบว่า เป็น elf 64 bit - No canary found - No PIE (0x400000)
Harshit·Dec 5, 2023Why gets() is bad / Buffer OverflowsThe gets() function in C is considered bad and unsafe due to its potential for causing buffer overflows. When using gets(), the function…
mirakiht·Oct 4, 2022Return To Shellcodesession นี้จะคล้ายๆ กับ return to win จากที่เรา return ไป ที่ address ของ function ที่เราต้องการ แต่เราจะ return ไปที่ address ที่เรา โยน…
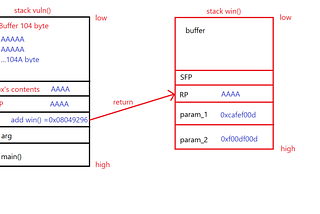
mirakiht·Oct 4, 2022Return To Winsession นี้เราจะพูดถึงการ ควบคุม return pointer ของ stack เพื่อที่เราจะสามารถ return ไปที่ func ที่เราต้องการ
mirakiht·Oct 4, 2022Modify variable’s value 2ต่อจาก Modify variable’s value 1 ที่เราทับค่า value ของ argument ใน main แต่ใน session นี้เราจะข้าม function และไป ทับ argument เลย…