Prasanth Kumar Malleboina·Oct 20Two Logs Agreed. But Did That Mean the Activity Was Malicious?Day 10 | My Journey into SOC Operations, Detection Engineering, and Incident Response
AartiDecode·Oct 7Fintech Cybersecurity & Fraud Prevention in 2026: Trends, Lessons Learned ReportFintech companies are all about real-time services and giving customers what they want: instant payments and onboarding and 24/7…A response icon1A response icon1
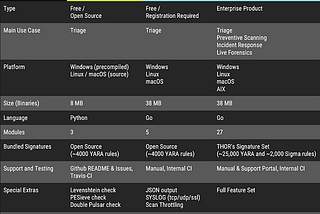
Mahim Avi·Oct 3How to scan systems with THOR lite scanner during compromise assessment and incident responseIn this post, I tried to consolidate information's of thor-lite that I think will be helpful for IR folks.
Soul Crancer·Sep 22Building a Polymarket TWAP Breakout Detection BotExplore how a Polymarket TWAP breakout bot detects crypto momentum, TWAP divergence, probability changes, liquidity conditions, and false…
Ysunita·Aug 25Can a Blood Test Catch Cancer Before You Feel Sick?Originally published on Lab to Lifestyle by Sunita — read the full piece, with sources and data, here.
Ramen Kumar Das·Aug 5Error Correction & Detection at Digital Communication SystemIn the context of Digital communication, the bit error is a very common phenomenon. The first question is, if the bit error happens, what…
Pravat Dash·Jun 10SigHunt — From IOCs to Sigma Rules: A Detection Engineering Walkthrough of TryHackMe — SigHunthttps://tryhackme.com/room/sighunt
MUHAMMAD MOIZ UD DIN RAFAY·May 7Advanced USB Monitoring and Data Exfiltration Detection with WazuhLab Environment Setup
Mohamed Elfayoumy·Apr 14From Simulation to Detection: Fileless PowerShell & Mimikatz Attacks using Atomic Red Team (MITRE…Atomic Red Team is an open-source adversary simulation framework developed by Red Canary, built on the MITRE ATT&CK framework. It enables…
InMeetCyberbyJinay·Mar 1Day 174 — Building a Data Wiping Detection Engine in 24 Hours (ISEA Hackathon)This weekend, I participated in a 24-hour ISEA Anti-Forensic Detection Hackathon.