Ilja Krasnjanski·Nov 2Building and Testing Detections for UNK_DeadDropThirty-three YARA rules replayed against retained artifacts, followed by a separate noise review and static scanner evaluation.
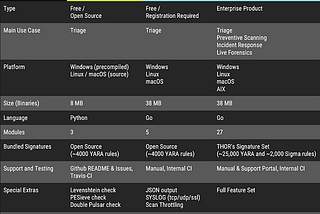
Mahim Avi·Oct 3How to scan systems with THOR lite scanner during compromise assessment and incident responseIn this post, I tried to consolidate information's of thor-lite that I think will be helpful for IR folks.
Ayush Malwarex·Sep 4Technical Deep-Dive: Analyzing Qakbot Version 2.7.23 (Campaign: BDNIMBUS)Executive Summary
InOSINT TeambyAdam Goss·May 19The Detection Engineering Lifecycle in 2026 (Sigma, YARA, DaC & AI)The fastest recorded breakout time in 2025 was twenty-seven seconds. That is the elapsed time between an attacker’s initial foothold and…
Jonathan H·Mar 7Hunting Threats with Precision: A Practical Guide to YARA Rules for DetectionStop chasing ghosts. Start writing rules that actually catch malware.